

Section 02
22. The Resilient Substrate: Hybrid Mesh–VLAN Convergence
The foundation of the architecture relies on separating logical security boundaries from physical infrastructure, so that trust zones survive changes in topology, carrier, or site.
2.1 Layer 2 Hardware Segmentation (RoaS)
Local infrastructure at geographically diverse nodes employs a Router-on-a-Stick configuration. Through 802.1Q tagging, sensitive development environments are logically isolated from general-purpose traffic across a single physical trunk link, allowing strict inter-VLAN policy enforcement without additional hardware at each site.
2.2 Layer 3 Overlay (P2P Mesh)
To bridge international sites without centralized VPN concentrators, the architecture deploys a P2P mesh built on WireGuard-class protocols with a control plane for coordination. This enables NAT traversal, dynamic path selection with automatic failover between carriers, and automated key exchange and rotation.
2.3 Carrying VLANs Across the Overlay
Because WireGuard operates at Layer 3, 802.1Q tags do not traverse it natively. Segmentation is preserved in one of two ways: by encapsulating Layer 2 frames (for example VXLAN or GRETAP) inside the encrypted tunnel, or by mapping each VLAN to a routed subnet and enforcing the same trust zones through overlay access policy. Either way, the zone boundary defined at one site is honored at every other site.
The result is a resilient, encrypted fabric that keeps cross-border development operations running through carrier outages and path degradation. It is not designed to be undetectable: WireGuard traffic has a recognizable handshake and can be identified by inspection. Its guarantee is confidentiality and integrity of the payload, not concealment of the tunnel.
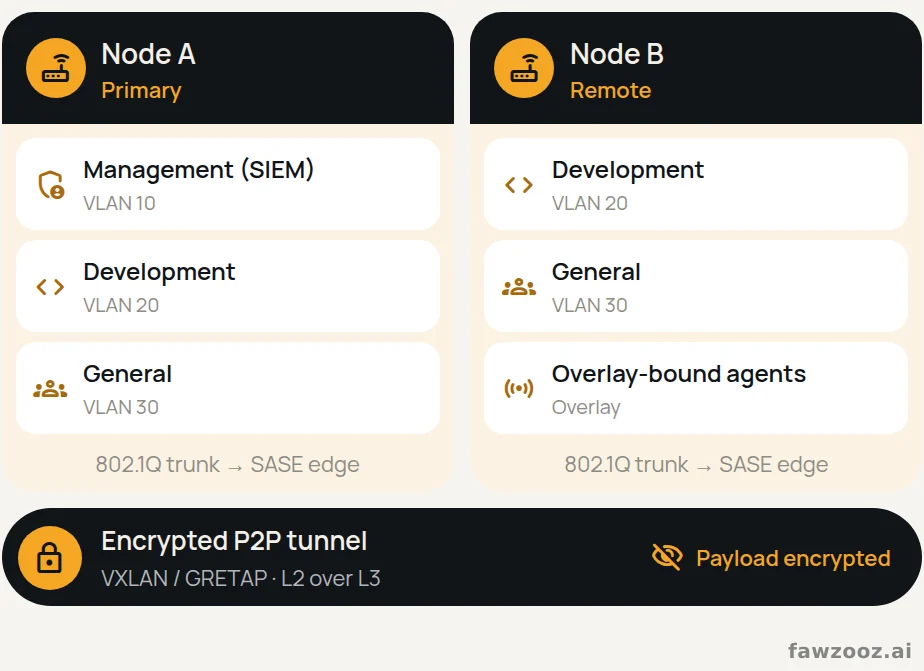
Text in this figure
Node A · Primary · Management (SIEM) · VLAN 10 · Development · VLAN 20 · General · VLAN 30 · 802.1Q trunk → SASE edge · Node B · Remote · Development · VLAN 20 · General · VLAN 30 · Overlay-bound agents · Overlay · 802.1Q trunk → SASE edge · Encrypted P2P tunnel · VXLAN / GRETAP · L2 over L3 · Payload encrypted
Tip: use ← → to move between sections.