

Section 6
6The Eleven Modules
Text in this figure
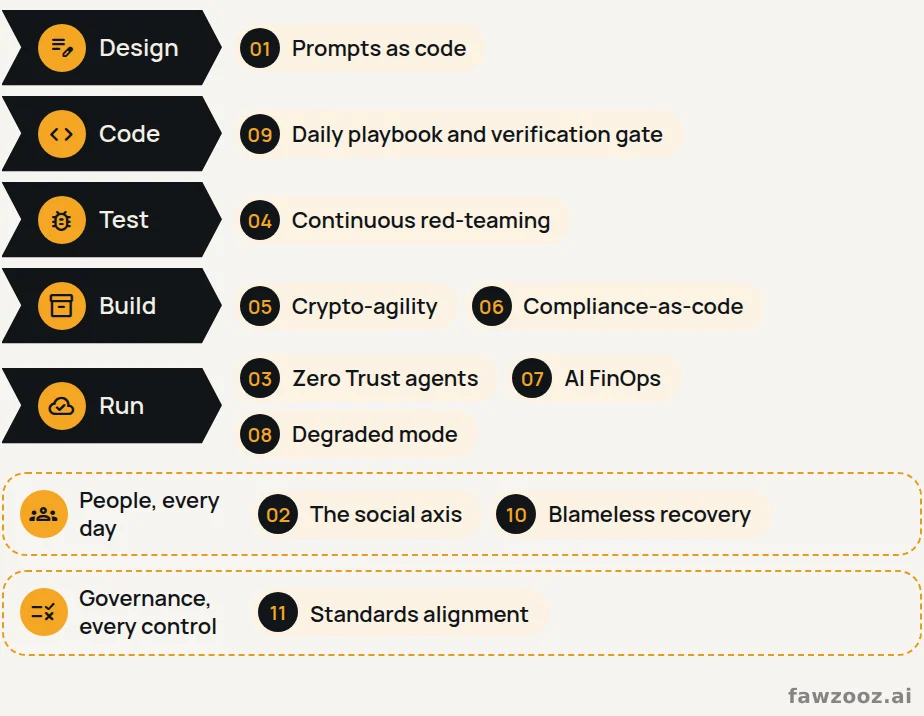
Design · 01 · Prompts as code · Code · 09 · Daily playbook and verification gate · Test · 04 · Continuous red-teaming · Build · 05 · Crypto-agility · 06 · Compliance-as-code · Run · 03 · Zero Trust agents · 07 · AI FinOps · 08 · Degraded mode · People, every day · 02 · The social axis · 10 · Blameless recovery · Governance, every control · 11 · Standards alignment · Figure 7. Where the eleven modules act along the delivery pipeline.
Module 01 of 11
Prompts as code
We treat prompts, system instructions and retrieval settings exactly like source code: versioned in Git, reviewed, and tested. Before anything merges, automated evaluation gates built on tools such as DeepEval and RAGAS check that answers stay faithful to their sources, relevant to the question and grounded in the right context.
Module 02 of 11
The social axis
The Scrum Master becomes what The Cognitive Firewall calls the Servant’s Shield: the person who protects the team from outside chaos. Every day ends with a 15-minute State-Save ritual, in which each developer writes down open loops, the hypothesis they were testing and exactly where they stopped. Closing the day on paper makes it easier to leave work at work.
Module 03 of 11
Zero Trust in the reasoning layer
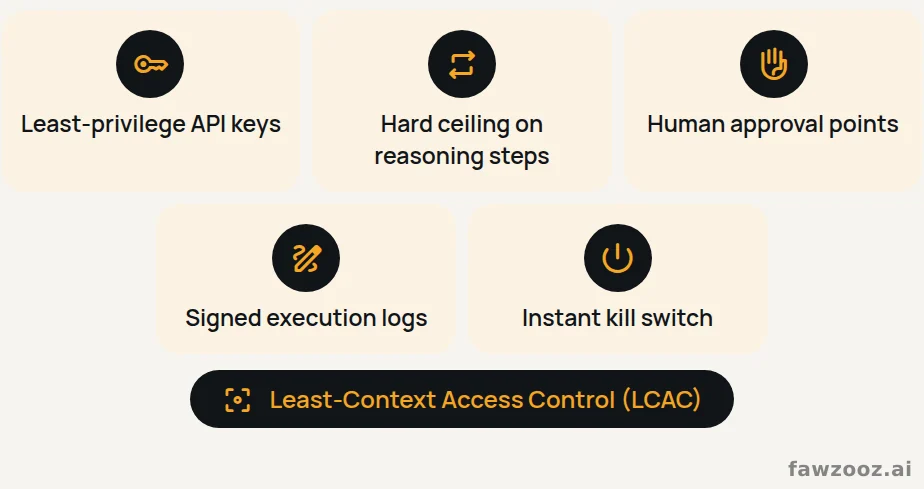
Agents get the least context they need for the task in front of them, an approach we call Least-Context Access Control (LCAC). Five constraints apply to every agent: API keys with the least privilege possible; a hard ceiling on reasoning steps (for example, ten loops); predefined points where a human must approve before the agent continues; signed execution logs; and a kill switch that stops the agent instantly.
Text in this figure
Least-privilege API keys · Hard ceiling on reasoning steps · Human approval points · Signed execution logs · Instant kill switch · Least-Context Access Control (LCAC) · Figure 8. The five constraints of Least-Context Access Control, applied to every agent.
Module 04 of 11
Continuous red-teaming
Adversarial testing runs inside the build pipeline. Before a pull request is approved, automated scripts try prompt injection, jailbreaks, context leakage and hallucinated dependencies against the change. If a guardrail breaks, the build stops.
Module 05 of 11
Crypto-agility in CI/CD
Scanners in the pipeline look through source code, dependencies and container images for RSA and elliptic-curve cryptography, and track the migration path to the NIST post-quantum standards published in 2024: FIPS 203 (ML-KEM) for key encapsulation, and FIPS 204 (ML-DSA) and FIPS 205 (SLH-DSA) for digital signatures.
Module 06 of 11
Compliance-as-code for third-party models
Every external model and open-source package entering the build is checked automatically. The pipeline flags licences that do not suit commercial use and records where training data comes from. This gives the evidence an organisation needs to show alignment with ISO/IEC 42001:2023 and the EU Artificial Intelligence Act (Regulation (EU) 2024/1689); it does not replace legal review.
Module 07 of 11
AI FinOps
We track token use, inference cost and the return on semantic caching for each deployment. A financial circuit breaker halts the pipeline when a change causes a sudden spike in model calls, which protects against the Unbounded Consumption risk in the OWASP Top 10 for LLM Applications (2025).
Module 08 of 11
Degraded mode
Every team has a written plan for the day its main AI provider is down, slow or rate-limited. Work falls back to smaller local models, or moves to a human review queue, so delivery slows down rather than stops.
Module 09 of 11
The developer’s daily playbook
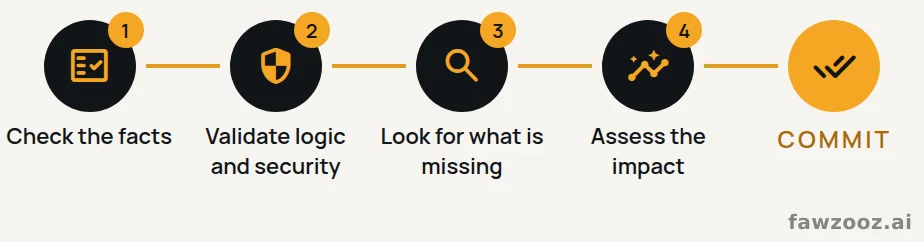
Developers register any new AI tool through an open intake register, which sorts it against a five-dimension risk taxonomy. A delegation matrix decides who may approve what, based on how easily an action can be reversed. And every AI-generated change passes a four-part verification gate before commit: check the facts, validate the logic and security, look for what is missing, and assess the impact.
Text in this figure
1 · Check the facts · 2 · Validate logic and security · 3 · Look for what is missing · 4 · Assess the impact · Commit · Figure 9. The four-part verification gate every AI-generated change passes before commit.
Module 10 of 11
Blameless recovery
After a serious incident, the team recovers without blame and returns to full pace in phases. Leaders hold regular Failure Swap sessions in which they share their own mistakes, including the times AI misled them, so that admitting an error becomes normal.
Module 11 of 11
Standards alignment
Each control maps to recognised standards: ISO/IEC 27001:2022 for information security, ISO/IEC 42001:2023 for AI management systems, ISO 45003:2021 as guidance on psychosocial risk, the NIST AI Risk Management Framework (AI RMF 1.0, 2023), and the EU Artificial Intelligence Act.
Tip: use ← → to move between sections.